Sender identity
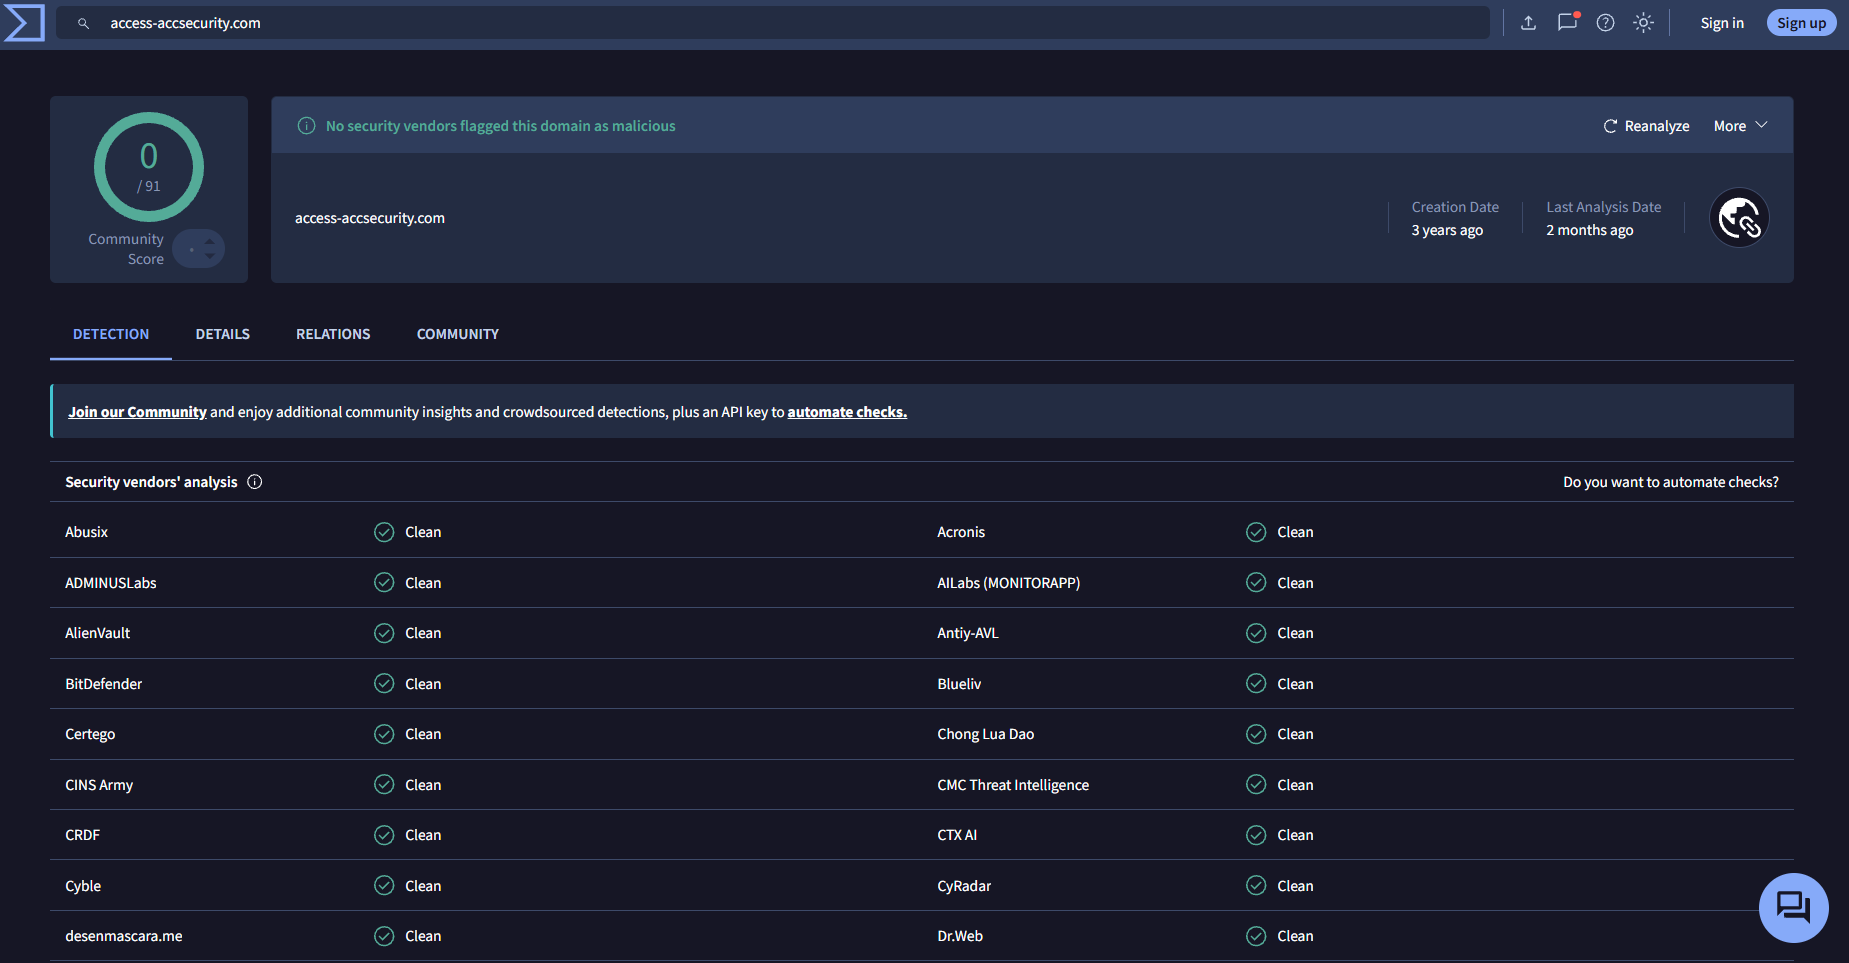
The email claims to be from Microsoft, but uses no-reply@access-accsecurity[.]com and an unrelated Gmail Reply-To address.
security lab / 01
completed 5 October 2026I analysed an email impersonating Microsoft, checking its headers, reply address and links alongside domain reputation. I then ran a separate, harmless local simulation and used Postfix logs to confirm which of five test mailboxes received it.
01 / overview
Is the archived email consistent with phishing, and how can server evidence reveal the full recipient scope of a controlled simulation?
This project combines two distinct exercises: a manual investigation of an archived phishing sample and a harmless, locally delivered simulation. The first develops the verdict; the second demonstrates how to trace who received a message.
02 / what I found
The email claims to be from Microsoft, but uses no-reply@access-accsecurity[.]com and an unrelated Gmail Reply-To address.
The recorded results are SPF none, DKIM none and DMARC permerror. These are assessed together with the message content; they are not described as an authentication fail.
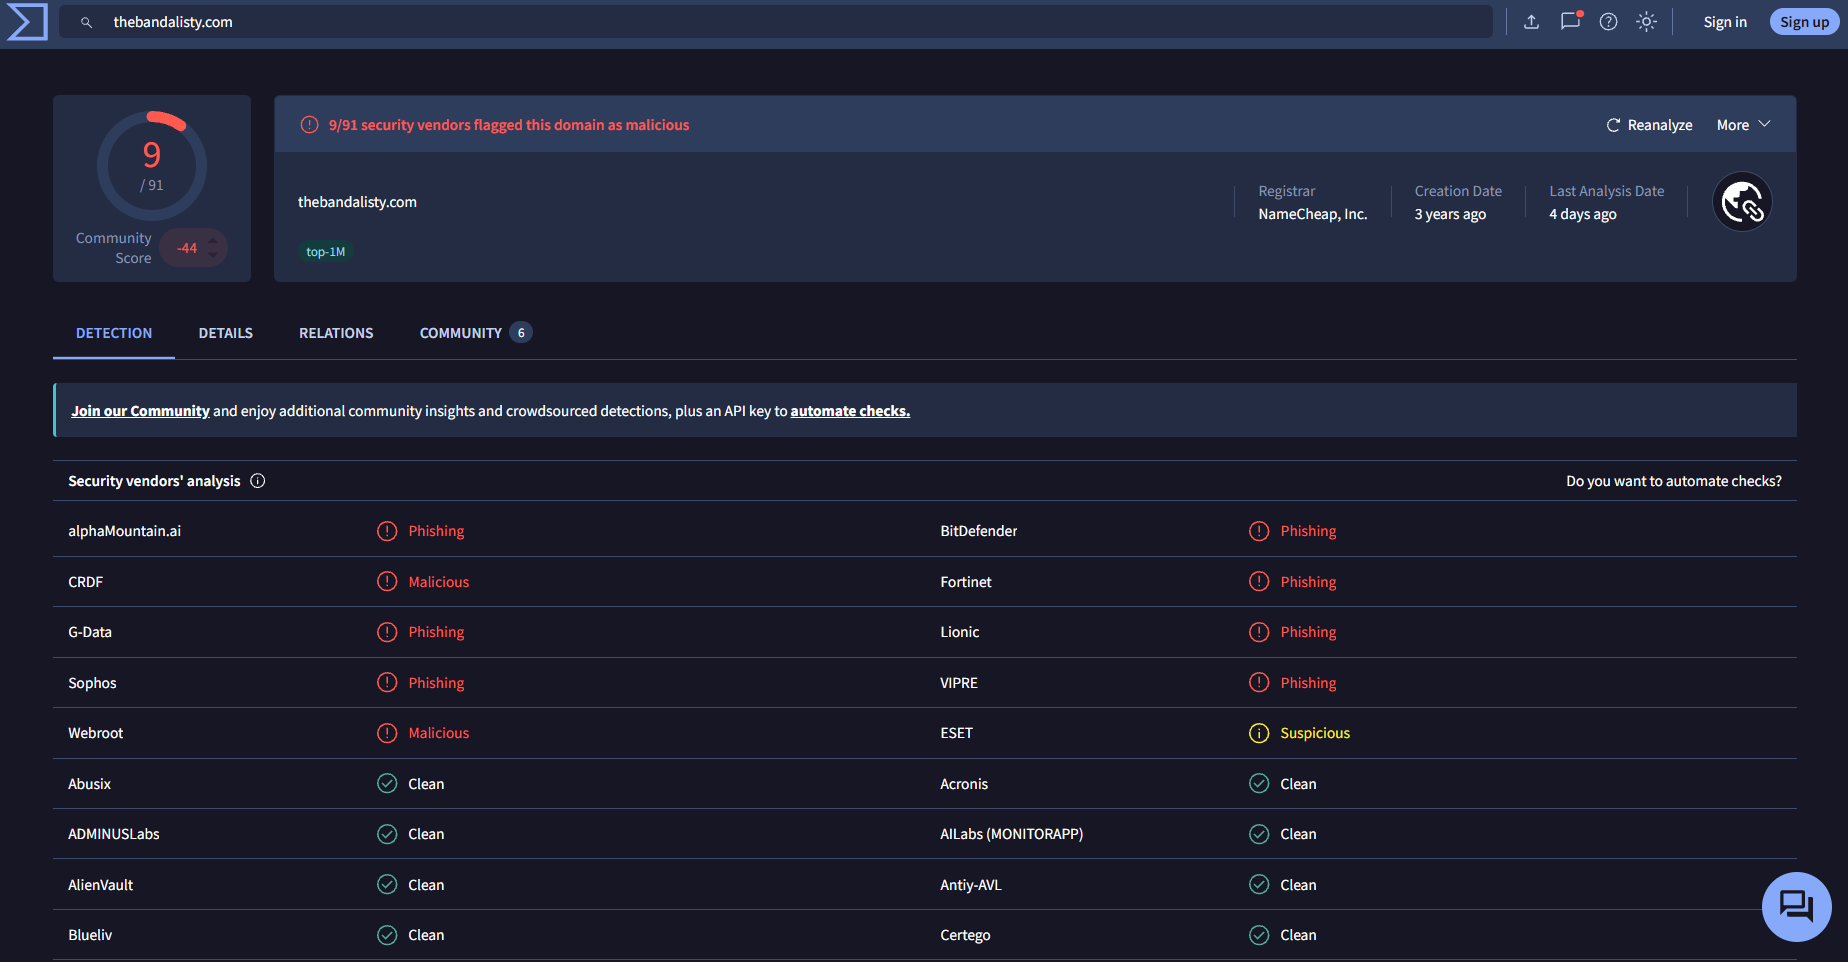
The three action links use mailto and direct messages to the unrelated Gmail address. A hidden image points to thebandalisty[.]com. No web sign-in or credential collection form was observed.
The separate local simulation shows three recipients in To/Cc and five delivered copies. Postfix records reveal Carol and Vittorio in addition to the visible recipients.
03 / evidence & scope
Archived headers and HTML, captured VirusTotal results, a prepared simulation message, native SMTP output, Postfix delivery records, five received Maildir copies and SHA-256 checksums.
The original archived email’s full recipients remain unknown. The simulation demonstrates delivery, not opens, clicks, replies or compromise. A reputation lookup from 2026 does not establish a domain’s reputation when the sample was delivered in 2023.
04 / reproduce the lab
The guide covers the archive review and a Ubuntu/Postfix environment with five local test recipients. SMTP is restricted to loopback and external delivery is disabled. The labelled simulation contains no credential form or live tracking service.